
 Song-saem: From Planner to Developer with AIBlog home →
Why Did Old PHP Websites Get Hacked So Often? Are Today’s Web Apps Safe?
Old PHP websites were usually hacked not because of PHP alone, but because unsupported versions, un-updated boards and plugins, and loose file-upload features piled up. Here are the gaps attacks came through, what changed with services like Vercel and Supabase, what is still your job, and the order in which to check an old site.
Why did old PHP websites get hacked so often? PHP alone doesn’t explain it. Unsupported PHP versions, board software and plugins that were never updated, and loose file-upload features often came together, and above all, many sites never decided who would look after them after launch. Services like Vercel and Supabase take over part of running the server, but keys and access rights, updates, and deciding who is in charge are still up to whoever built the app.
Is PHP a bad language?
Not necessarily. PHP is still in use, and it can be run safely on a current version with sensible settings. On the other hand, a site built in any other language runs into trouble too if updates and upkeep are neglected.
Old websites sometimes combined an unsupported PHP version, un-updated boards and plugins, and a loose file-upload feature. Versions past their security support no longer get fixes for newly found vulnerabilities. Just as a house that was fine when built doesn’t stay fine on its own, a website needs someone named to look after it.
Which gaps did attacks come through?
| Gap | How attackers get in | How to block it |
|---|---|---|
| Outdated boards and plugins | Once a vulnerability is known, attackers use automated tools to find sites running that software | Update them, and remove plugins you don’t use |
| File uploads | A malicious file that looks like an image is uploaded and the server runs it as a program. Such a file used to control a server remotely is called a web shell | Make sure uploaded files can’t run as programs |
| SQL injection | Text typed into an input box is read as part of a database command | Handle input separately from commands |
| Weak passwords | Attackers guess admin or file-transfer (FTP) account passwords | Use long passwords and multi-factor authentication, and remove unused accounts |
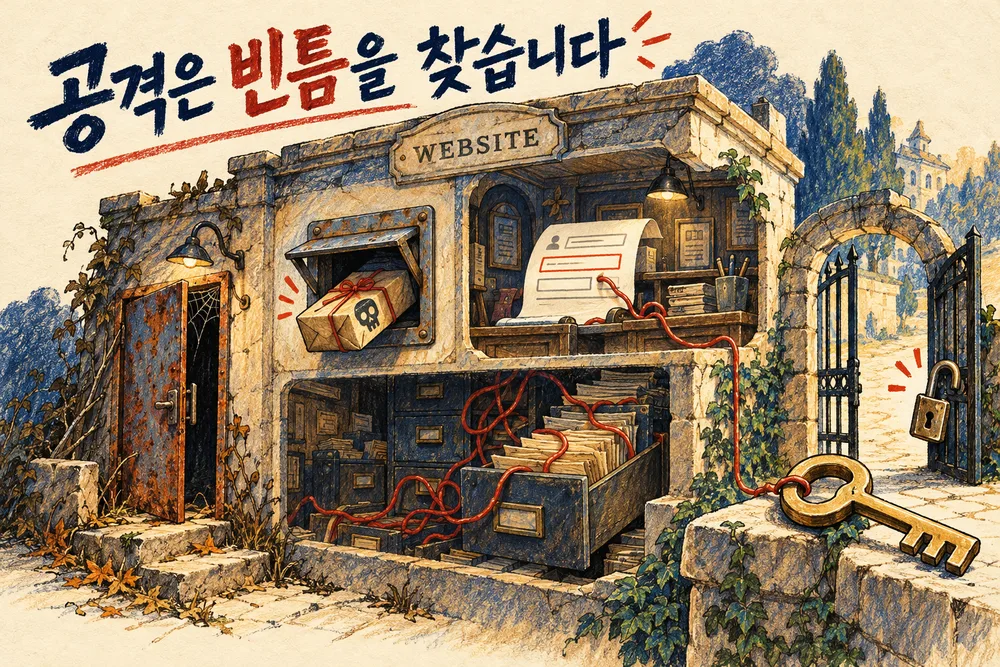
What matters here is the gap, not the size of the site. It’s hard to assume “who would bother hacking a small site like ours?” Attack tools look for vulnerable software and settings, not for who runs the site.
What changed with today’s approach?
With services like Vercel and Supabase, you can hand part of running the server and managing the database to the service company. It has also become easier to separate where the app runs, where files are kept and where data is stored. That means less to install and manage yourself.
That said, many hosting companies managed servers in the old days too, and PHP services today can also run in managed environments. It’s less a contest between PHP and new technology than a difference in structure: who manages what.
What is still yours to look after?
| What to look after | Details |
|---|---|
| Keys and access rights | Never put powerful keys, such as Supabase’s secret key, in page code or a public repository. Set access rules like RLS on the data your app reaches, and check that other people’s records don’t show up |
| Updates | New technology has vulnerabilities too. In December 2025, a serious vulnerability was disclosed in some of React’s server features |
| Who is in charge | Decide who checks when something goes wrong, what gets backed up and who updates. If you built the app alone, that role is yours |
Building with new technology doesn’t mean you can skip updates. I also covered keys and access rules in Part 6 of Build Your Own Scheduler.
If you have an old website, where do you start?
- Before changing any software, back up your files and database, and check that you can actually restore them.
- Look at the versions of PHP, board software and plugins. Some features of an old site may break on new versions, so test in a separate environment first if you can.
- Remove plugins and accounts you don’t use, and make sure uploaded files can’t run as programs.
- Use a long password for admin accounts, and turn on multi-factor authentication if it’s supported.
- If it’s hard to judge yourself, ask your hosting company or, in Korea, look into KISA’s website security service for small businesses.
- If you already suspect a hack, don’t start by deleting files; get advice from your hosting company or KISA (118 in Korea).
What should you ask AI?
If you have the code of a website you manage, you can ask an AI coding tool to check it before asking it to fix anything.
“Look at this website’s PHP version, the list of board software and plugins, and the code that handles file uploads and the database. Separate the problems you confirmed from the parts that need more checking. Don’t change anything yet; first explain how to back up and the order of fixes.”
AI won’t necessarily find every problem. The settings of a running server sometimes can’t be seen from the code alone. Double-check versions and security notices against official sources, and don’t paste passwords or secret keys into the chat. I wrote about that habit in Why Is AI So Confidently Wrong?.
In short
- Old PHP websites were usually hacked less because of the language than because unsupported versions, un-updated boards and plugins, and loose upload features piled up.
- Attack tools look for gaps, not for the size of the site.
- Services like Vercel and Supabase take on part of running the server, but keys and access rights, updates and deciding who is in charge are still yours.
- For an old website, start with a backup and a restore check, then check versions, clean up, block uploads from running and tighten passwords.
At ONE-PEX, building the business system FROX, we think the more a service handles company data, the more it matters not only what it’s built with, but who looks after it and how.
Sources (checked 2026-10-27)
- PHP, Supported Versions
- OWASP, File Upload Cheat Sheet
- OWASP, SQL Injection Prevention Cheat Sheet
- KISA Boho, SME website security service
- Supabase docs, API keys
- Supabase docs, Shared responsibility model
- React blog, Critical Security Vulnerability in React Server Components (2025-12-03)
Related reading: How Have Website Databases Changed? · Part 6: Connecting saving and login · Why Is AI So Confidently Wrong?

A software planner who became a developer after two years of working with AI five to twelve hours a day. Today I build FROX, an AI-powered business system, at ONE-PEX.
More posts
- What Can You Build with AI?Orders in KakaoTalk, Stock in Excel, Receivables in a Notebook: Changing Messenger Orders Only the Owner Understands (Food Supplier, Part 1)
- What Can You Build with AI?I Fixed My TWA App, So Why Didn't It Change? What I Learned from the War with Caching
- What Can You Build with AI?Details Matter: Splitting 3D Characters and Vehicles So They Can Move (Building Road Voca 2, Part 5)